NOTE
“AI is a corporate risk. Non compliant AI is unmanageable corporate risk” - © Dusan Jovanovic 2026
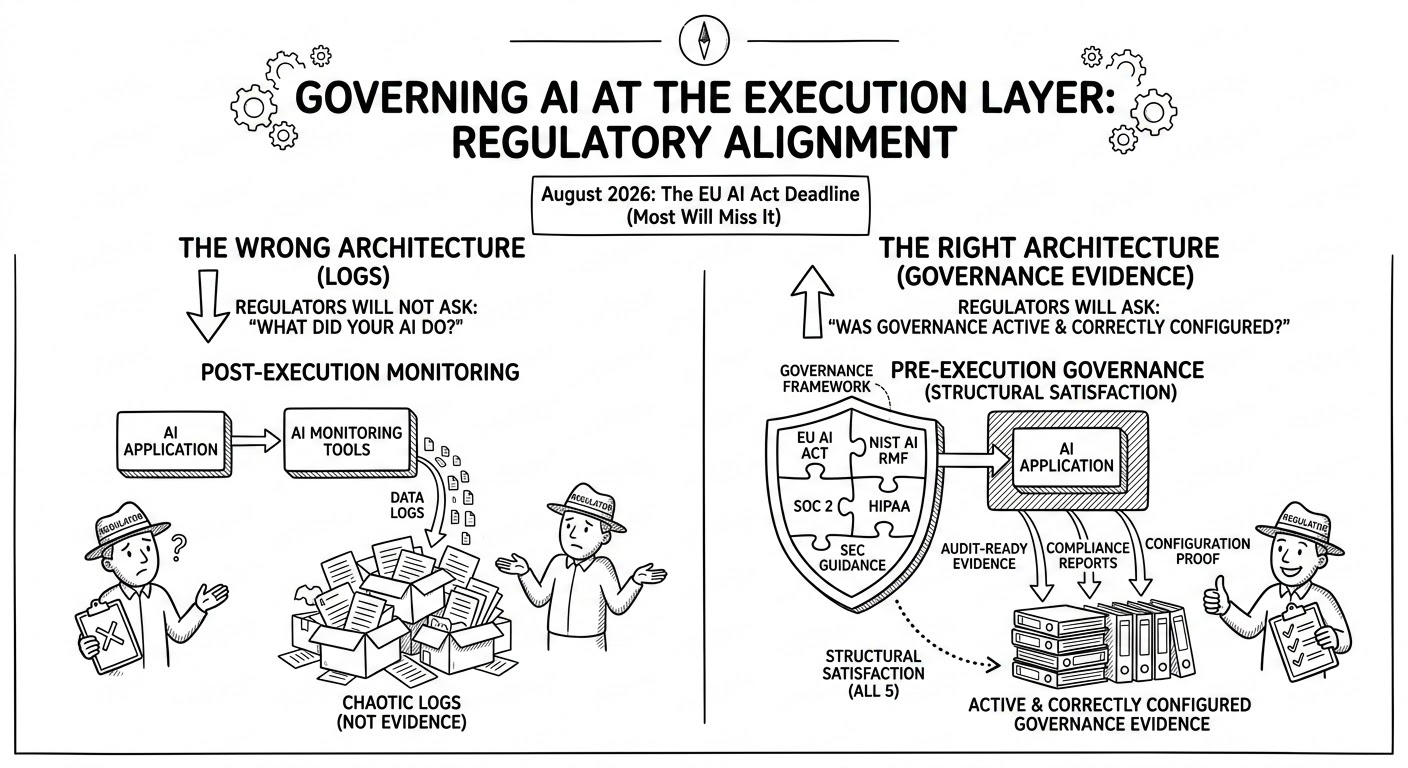
The EU AI Act compliance deadline for high-risk AI systems is August 2026.
Most will miss it because because their AI monitoring tools produce logs, not governance evidence.
Regulators won’t ask what your AI did. They will ask whether governance was active & correctly configured. Those are architecturally different questions requiring architecturally different systems.
What exactly what each framework requires:
- EU AI Act
- NIST AI RMF
- SOC2
- HIPAA
- SEC guidance
At DBJ.ORG, we recommend closed-loop, pre-execution and runtime-integrated governance framework
NOTE
Governing AI at the Execution Layer: Regulatory Alignment
(pobably not a lucid and succinct text: https://lnkd.in/egw4eCC2)